WebMCP for Ecommerce: Make Storefronts Agent-Ready Without Rebuilding Checkout
A practical guide to browser-native tools, backend MCP bridges, testing, security, and merchant control
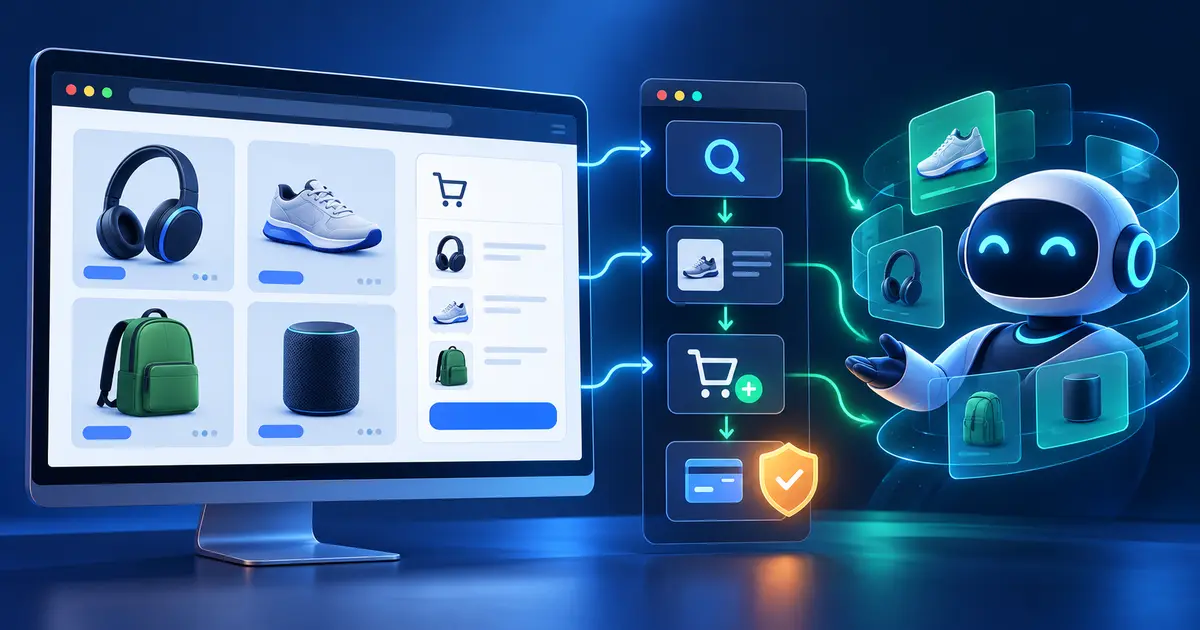
WebMCP is moving from a browser experiment into a practical commerce deployment. On October 21, 2026, Cloudflare and Commerce.com announced that WebMCP support would be made available across a network serving almost 100,000 commerce domains. Their implementation exposes product search, product details, cart actions, and checkout-link creation to compatible browser agents—without asking every merchant to rebuild its storefront.
That makes WebMCP timely, but it does not make it finished. Chrome still describes the technology as a proposed web standard, its current specification is a Community Group draft rather than a W3C Standard, and production support remains uneven. The useful question is therefore not “Will WebMCP replace websites?” It is: Which high-intent storefront tasks should you expose now, how should you test them, and where must a human remain in control?
What changed on October 21, 2026
The new Commerce.com deployment gives WebMCP a concrete ecommerce reference point. According to the companies, a compatible agent can discover tools that search a catalog, inspect a product, build a cart, and generate a checkout link. The shopper remains on the merchant's storefront and completes checkout there. Cloudflare says the tools run in the active browser session, so the agent sees the same session-dependent prices, inventory, and cart state as the shopper.
The rollout also illustrates a deployment shortcut. Cloudflare's edge implementation can inject a small browser-side script and translate existing backend Model Context Protocol (MCP) definitions into WebMCP tools. Its API documentation exposes a webmcp_enabled zone setting, an optional backend MCP URL, and installable tool packs. The capability is still labeled beta, so availability, compatibility, and operating limits should be confirmed for each account before planning a launch.
Fact: this is a real platform deployment tied to almost 100,000 domains. Inference: it may accelerate merchant experimentation because a platform can provide common tools centrally. It is not evidence that all of those storefronts have enabled the feature, that all AI agents can use it, or that WebMCP improves search rankings.
WebMCP in one minute
WebMCP lets a page publish structured tools to an AI agent operating in the browser. Instead of inferring every action from buttons, labels, and page layout, the agent can discover a named operation with a description and a JSON Schema input contract. The page then handles the operation using its existing JavaScript, DOM state, session, and business APIs.
Chrome documents two authoring paths:
- Declarative tools annotate ordinary HTML forms. This is a progressive-enhancement path for tasks already represented by forms.
- Imperative tools register JavaScript handlers through
document.modelContext. This suits richer workflows that need application logic, validation, or structured results.
The important boundary is the browser tab. WebMCP tools can use the user's authenticated session and visible page state, but they are ephemeral: when the tab closes or navigates away, the tools disappear. Sensitive actions can still require an explicit user confirmation in the interface.
WebMCP is not a replacement for MCP
| Question | WebMCP | Backend MCP |
|---|---|---|
| Where does it run? | In the active browser page or tab | On a server or local MCP host |
| What context can it use? | DOM, current page state, cookies, and browser session | Server-side data and explicitly configured credentials |
| How long does it exist? | Usually for the lifetime of the page | Persistent beyond one tab |
| Best fit | User-facing actions in the current web experience | Cross-application or backend capabilities |
| Typical commerce example | Add the visible product to the current cart | Query catalog, inventory, or order systems |
The two layers can complement each other. A backend MCP server can define durable catalog or order operations; a storefront can expose a smaller, session-aware subset through WebMCP. Cloudflare's bridge is one implementation of that pattern. For a broader backend integration example, see Rubic8's guide to MCP with Apigee hybrid and Kubernetes.
A practical storefront tool map
Start with actions that have clear intent, deterministic inputs, and reversible outcomes. Do not turn every button into a tool.
1. Search products
Accept a query plus constrained filters such as category, maximum price, color, and size. Return product IDs, names, current prices, availability, and canonical URLs. Keep the result small and structured. A tool that returns an entire rendered page is harder for both agents and developers to validate.
2. Get product details
Use a stable product or variant ID. Include facts that affect the buying decision: price, currency, stock status, options, delivery constraints, and the canonical product URL. Do not let the agent invent compatibility or availability from marketing copy.
3. Add an item to the cart
Require a product or variant ID and a bounded quantity. Return the resulting line item and cart summary. Make the operation idempotent where possible, or accept an idempotency key, so a retry does not silently add the same item twice.
4. Prepare checkout
Generate or navigate to a checkout page, but keep purchase confirmation, payment, shipping-address review, and acceptance of recurring terms in the human-visible flow. This boundary makes the feature useful without turning an ambiguous agent request into a financial commitment.
Minimal implementation patterns
A conventional form can be enhanced declaratively. The exact attributes and behavior remain experimental, so test against the Chrome build and origin-trial documentation you plan to support.
<form
  toolname="searchProducts"
  tooldescription="Search products by query and maximum price">
  <label>
    Query
    <input name="query" required />
  </label>
  <label>
    Maximum price
    <input name="maxPrice" type="number" min="0" step="0.01" />
  </label>
  <button type="submit">Search</button>
</form>
For an imperative tool, register a narrow contract and route the call through the same validated application service used by the visible interface:
await document.modelContext.registerTool({
  name: "searchProducts",
  description: "Search the current storefront catalog",
  inputSchema: {
    type: "object",
    properties: {
      query: { type: "string", minLength: 2, maxLength: 80 },
      maxPrice: { type: "number", minimum: 0 }
    },
    required: ["query"],
    additionalProperties: false
  },
  execute: async ({ query, maxPrice }) => {
    const response = await fetch("/api/products/search", {
      method: "POST",
      headers: { "Content-Type": "application/json" },
      body: JSON.stringify({ query, maxPrice })
    });

    if (!response.ok) throw new Error("Product search failed");
    return response.json();
  }
});
This client-side schema improves discoverability; it is not a security boundary. Validate every field again on the server. The API must enforce authorization, inventory limits, price calculations, and business rules independently of the tool description.
During development, inspect schemas and sample payloads with Rubic8's JSON Formatter and reject malformed contracts with the JSON Validator.
Security: treat tool metadata and outputs as untrusted
Chrome's agent-security guidance highlights two different risks. A malicious page can publish deceptive tool names or descriptions, and a legitimate tool can return content containing an indirect prompt injection. An agent should not treat either source as trusted instructions.
For the merchant, a defensible checklist is:
- Keep tools narrow. Prefer
addCartItemover an unrestricted “run storefront action” function. - Use strict schemas. Set length, range, enum, and additional-property constraints, then repeat validation server-side.
- Respect authorization. A browser session may identify the shopper, but it does not grant permission to bypass account, inventory, geographic, or age restrictions.
- Protect state changes. Preserve CSRF defenses, require idempotency for retry-prone calls, and apply rate limits.
- Separate reading from commitment. Search and product-detail tools can be low risk; payment, subscription, account changes, returns, and address updates need visible confirmation.
- Constrain origins. Avoid fetching arbitrary URLs or forwarding untrusted content to unrelated services.
- Log the path. Record tool name, schema version, validation outcome, affected resource, user confirmation, and result—without logging secrets or full payment data.
- Design safe errors. Return actionable error codes without revealing internal stack traces, credentials, or hidden inventory data.
Agents also need defenses such as tool allowlists, output-size limits, cross-origin restrictions, and a clear distinction between data returned by a tool and instructions the agent is authorized to follow. WebMCP improves structure; it does not remove the need for threat modeling.
WebMCP does not replace SEO, structured data, or accessibility
WebMCP is an actuation layer for browser agents. It is not, by itself, a search-ranking signal, an AI-citation guarantee, or a substitute for an indexable storefront. No official source cited here claims a ranking benefit.
Continue to serve useful HTML, stable canonical URLs, accurate product data, descriptive headings, accessible form controls, and supported Schema.org markup. Maintain XML sitemaps and merchant feeds where appropriate. WebMCP should be progressive enhancement: shoppers and crawlers that do not support it must still receive a functional site.
The distinction is practical. SEO and AEO help a system find and understand a product page. WebMCP helps a compatible browser agent take a structured action inside that page. Use the ChatGPT Search discovery checklist for publisher visibility work; use WebMCP for the task layer.
How to test WebMCP today
Chrome's documentation lists an origin trial for Chrome 149 and a local testing flag at chrome://flags/#enable-webmcp-testing. The Chrome DevTools WebMCP panel can list registered tools, show input schemas, execute them with test parameters, and surface results or errors. Because the feature is experimental, confirm version requirements against the current documentation before each release.
- Inventory the ordinary journey. Verify search, variants, cart, and checkout without WebMCP first.
- Register one read-only tool. Confirm that it appears only on the intended page and disappears after navigation.
- Validate the contract. Test empty strings, overlong input, negative prices, unknown properties, invalid variants, and unexpected currencies.
- Compare states. Ensure the tool and visible UI produce the same price, stock, cart, tax, and shipping results.
- Exercise retries. Repeat state-changing calls and confirm idempotency or duplicate-action protection.
- Test hostile content. Put instruction-like text in product titles, descriptions, reviews, and tool results; verify that it remains data.
- Verify confirmation gates. Make sure an agent cannot place an order, start a subscription, or change an account without an explicit human step.
- Test the fallback. Disable experimental support and confirm the storefront still works normally.
Should your team adopt it now?
Experiment now if you control a transactional web app, already have stable APIs, can run an origin-trial or controlled-browser test, and have security owners for agent-driven actions. Start with read-only discovery or reversible cart operations.
Wait if your checkout logic is fragmented, prices differ unpredictably across layers, your site depends on implicit UI state that APIs cannot reproduce, or your team cannot monitor tool calls. Fixing those foundations will help both WebMCP and conventional automation.
Avoid promising universal support. The standard, browser implementation, and vendor integrations are still developing. Publish a capability matrix for the browsers and agents you actually test, and version your schemas so future changes do not silently break callers.
The bottom line
The Commerce.com rollout is the strongest public signal yet that WebMCP can move beyond demos into large ecommerce platforms. Its near-term value is not an invisible autonomous purchase. It is a clearer contract between a storefront and a browser agent: searchable products, reliable product facts, reversible cart actions, and a checkout handoff the shopper can review.
Build that narrow path first. Keep the website usable without it, validate every input on the server, treat page and tool content as untrusted, and reserve consequential actions for the human. That approach is useful today even if the WebMCP specification changes tomorrow.
Official sources
- Cloudflare: How Commerce.com and Cloudflare are getting storefronts ready for AI agents — October 21, 2026
- Chrome for Developers: WebMCP overview and implementation guide — updated October 7, 2026
- Chrome for Developers: WebMCP compared with MCP
- Chrome for Developers: Security guidance for web agents
- Chrome DevTools: Test and debug WebMCP tools
- Cloudflare API: WebMCP zone settings
- WebMCP Community Group Draft
Rubic8 Editorial Team
Editorial Team
Rubic8 creates practical guides and free tools for developers, webmasters, and digital publishers. Our fast-changing technical content is reviewed against current primary documentation before publication.
